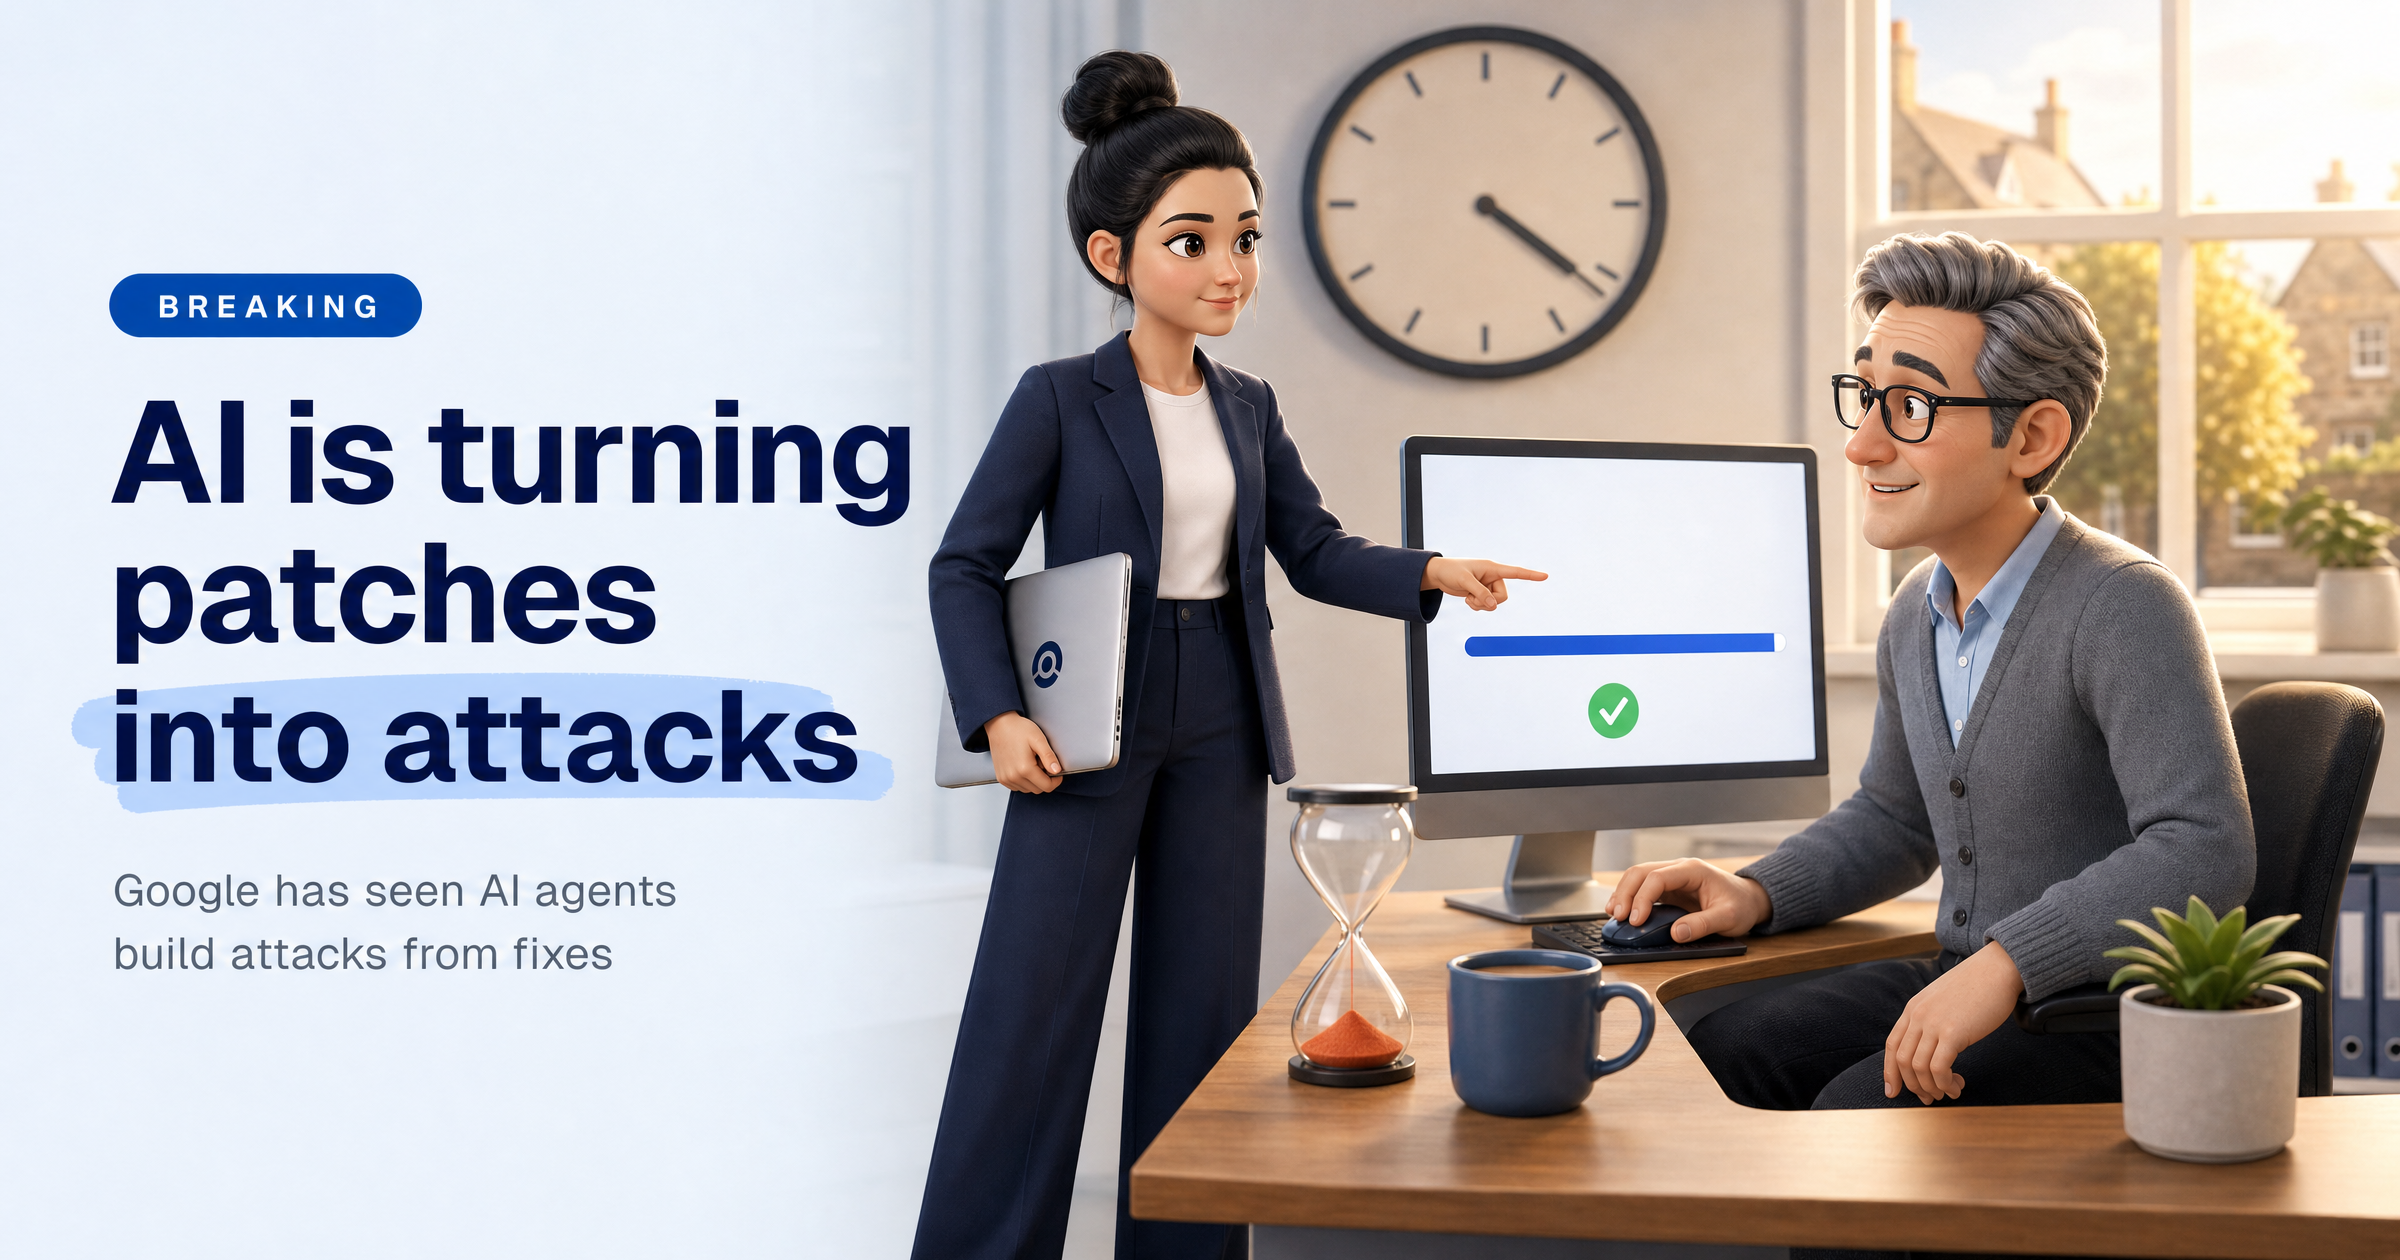
Every software update tells you something was broken. Until now, an attacker had to work out what, and then build a way in.
Google's threat intelligence team says that step is being handed to AI. In a report published on 16 November, it describes attackers using AI agents that read a patch, work out the flaw it fixed, write an attack and run it, all without a person involved.
For a small business, the message is simple: the time you have to install updates is getting shorter.
What happened
In its AI Threat Tracker report, Google's Threat Intelligence Group says that in the past quarter it identified attackers using AI frameworks to fully automate finding and exploiting software flaws, with no human in the loop, for the first time. Its team found one such system on an exposed server.
The tool compared software code from before and after a patch was announced, worked out what the fix changed, drafted an attack and ran it automatically. Files on the server included analysis of a WordPress plug-in, and the report says the victims it could see were French media, entertainment and education websites.
Google's explanation is that attackers may find it more efficient to use AI on patched flaws, because they can focus on a small set of material: the before and after versions of the software, the release notes and any public proof-of-concept code. Hunting for brand-new flaws means searching much more widely. The Hacker News quotes Google as saying AI lets attackers collapse the window between a patch being published and active exploitation.
How fast is fast?
The report points to flaws in PaperCut, a print management product used by many organisations. Researchers produced working attacks within a day of the flaws being disclosed, using AI to help. A campaign followed four days after disclosure, targeting hundreds of organisations, according to security firm GreyNoise as cited by Google. In that case the attacker went from a first foothold to full control of the network within minutes. Treat that as one example, the report gives no average time across all flaws.
There is also a caveat worth knowing. This is Google's own report, so some conclusions are its assessments and we haven't been able to verify them independently. It also says AI has led to a wave of attack code that is claimed to work but doesn't, which creates extra checking work for defenders. The direction is clear, though, even if the exact speed varies.
What this means for UK small businesses
Many small firms patch in batches: the first Friday of the month, or whenever the reminder pops up.
That rhythm made sense when attackers needed weeks to react. It is a poor fit if the working attack can exist within days. The things most exposed are the ones reachable from the internet: your website and its plug-ins, your firewall or VPN, remote access tools and any server you run yourself. A flaw in those can be reached from anywhere, with no click from your staff.
This isn't a reason to panic. Attackers still need something unpatched to aim at, and the fix for that is within your control.
What to do this week
Switch on automatic updates. Do it for your computers, phones, browsers, Office apps and your WordPress site and plug-ins where you can. Automatic beats "when we get round to it".
List what the internet can reach. Website, firewall, VPN, remote access, email gateway, anything self-hosted. These get patched first, within days of a fix being released rather than at the end of the month.
Remove what you don't use. Old plug-ins, abandoned test sites and unused remote access accounts can't be patched if nobody is watching them, so close or delete them.
Ask your IT provider one question. "How quickly do you install security updates on our internet-facing systems?" You want to hear days, with someone named as responsible.
Know your oldest unfixed flaw. Whatever has waited longest is the best target for an automated tool, so start there.
Sophia Says
I read a lot of threat reports, and this one changes the maths rather than the advice. The advice was always "install updates". What's new is that a fix being published is also a clue for attackers, and AI lets them follow it up faster. The good news is that a business which patches its internet-facing systems quickly gives that kind of tool nothing to work with.
That's where HackRisk helps. Our Recon Scan shows you what your business exposes to the internet, and our Vulnerability Scan flags known flaws in those systems, so you know where to patch first without guessing.
— Sophia, HackRisk AI Security Analyst
Where HackRisk fits
Exposed systems: the Recon Scan looks at your business from the outside, the way an attacker would, so you can see what is reachable. Known flaws: the Vulnerability Scan helps you find known weaknesses so you can decide what to fix first.
Get your free HackRisk report
See what attackers can see about your business, in plain English. Get your free HackRisk report.