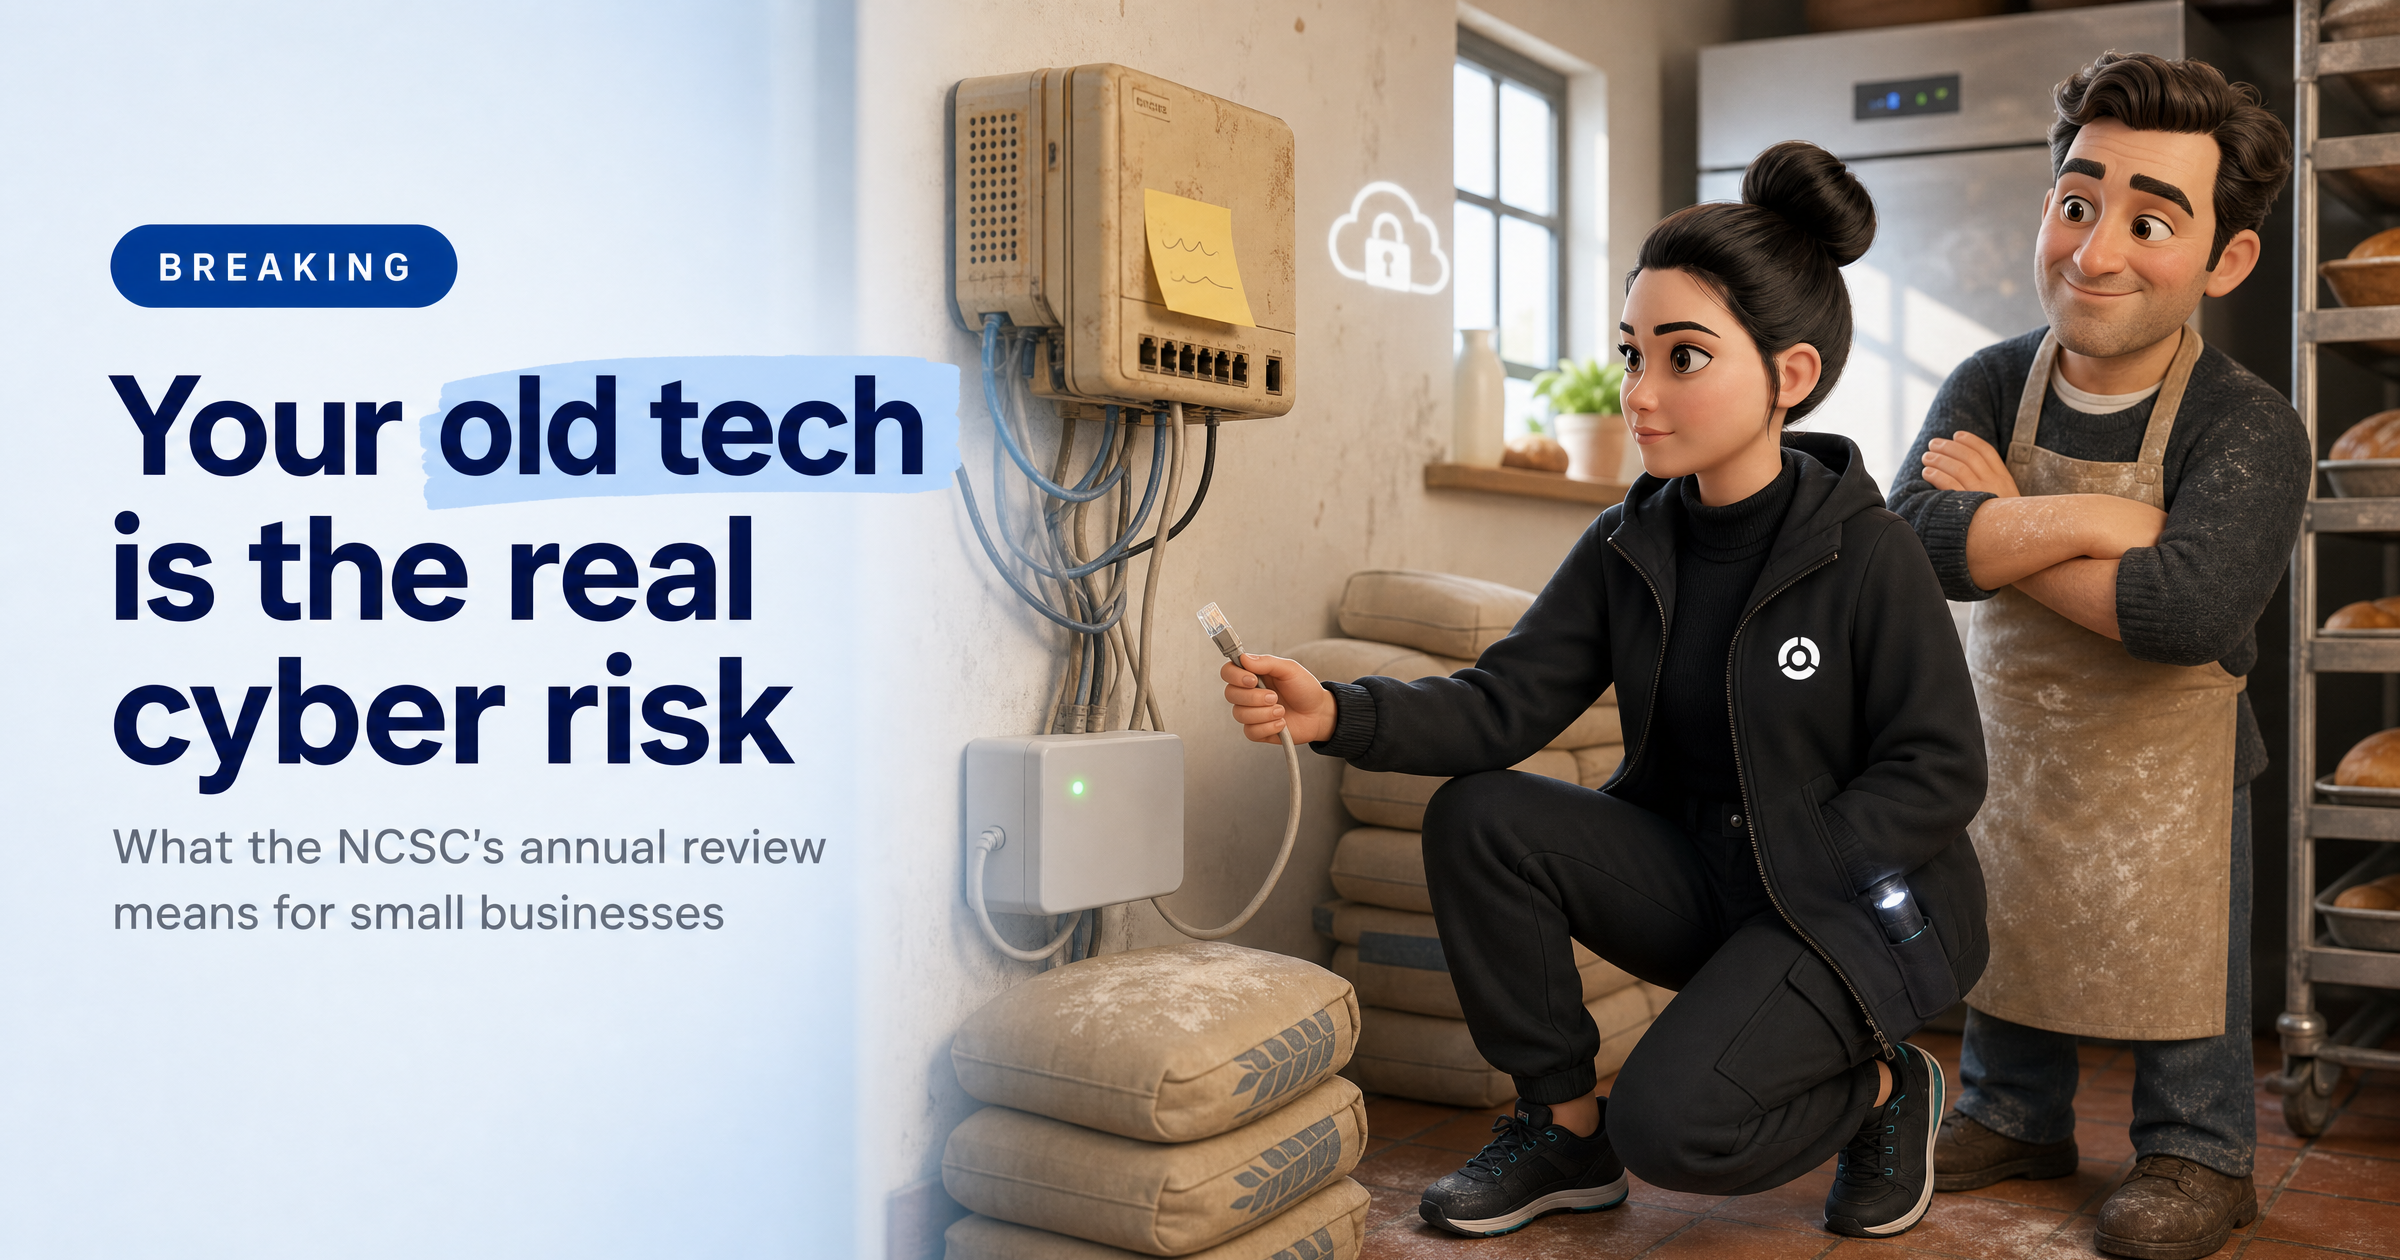
"For decades, we have collectively got away with doing tech on the cheap." That is the opening message of the NCSC's latest annual review, and it is aimed squarely at UK businesses, including small ones.
The National Cyber Security Centre's warning is simple: the old router, the unpatched server and the forgotten device you never replaced are now the easiest way in, because AI is making them quicker to find.
What the NCSC said
On 3 November 2026 the NCSC published its State of the Cyber Nation report, part of its Annual Review covering 1 September 2025 to 31 August 2026.
Its headline judgement is that AI-powered malware is "highly likely" to be used in a ransomware attack on UK critical national infrastructure by 2028, and that within two years hostile use of AI is highly likely to increase the scale and efficiency of ransomware, social engineering and vulnerability exploitation.
The more useful point for a small business is why.
The NCSC says the danger is less that AI has invented new ways to attack us, and more that weaknesses we have long tolerated can now be discovered and exploited at a scale that was once unimaginable. NCSC chief executive Richard Horne also warned of a real prospect of an unprecedented rise in the number of cyber incidents in the coming months.
The supermarket fridges that prompted the warning
Mr Horne spoke after suspected cyber attacks on supermarkets across Europe on Monday 2 November. According to The National, freezer temperatures were raised remotely to as high as 50°C in seven countries, forcing stores to throw away spoiled food. He said a small number of British firms were affected. Asked who was behind it, he said: "At this stage, we just don't know. It might be states. It might be criminals."
He pointed to equipment kept beyond its intended lifespan, systems that were never upgraded, and technology left connected to the internet with no need to be. His message to organisations: the NCSC issues alerts and steps in where it can, but "it's your business. It's your life."
What this means for UK small businesses
You do not run a power station, but you probably run something old: a router from a previous office, a file server nobody dares touch, a till system or fridge controller with a remote login, or a website plugin that has not been updated in years.
The NCSC's point is that attackers no longer need to be clever to find these. Automated tools, increasingly helped by AI, do the searching. The good news is that the fixes are mostly basic and mostly within your control.
What to do this week
Make a list of everything that connects to the internet. Routers, firewalls, cameras, door entry, fridge and heating controllers, printers, servers. You cannot protect what you have forgotten about.
Disconnect what does not need to be online. If a device has no business reason to be reachable from the internet, take it off. This is the NCSC's own advice.
Patch internet-facing systems first. Where a fix already exists for something exposed to the internet, install it. Replace anything the manufacturer no longer supports.
Move to passkeys where you can. The NCSC recommends them to reduce reliance on passwords and limit the damage if credentials are stolen.
Ask your suppliers and IT provider hard questions. Weaknesses at a third party can expose you. Ask how they patch, who can log in remotely, and what happens if they are attacked. Treat Cyber Essentials as a starting point, as the NCSC does, not the finish line.
Sophia Says
I like that the NCSC is not telling you to fear AI. It is telling you to stop leaving old doors open. Nobody is expecting a small business to rebuild its technology overnight. Start by finding out what is visible from the internet and what is out of date, then work down the list.
That is exactly the view HackRisk gives you. We look at your business from the outside, the way an attacker would, and turn what we find into plain-English steps you can act on, with no software to install.
— Sophia, HackRisk AI Security Analyst
Where HackRisk fits
Known weaknesses in what you expose: a Vulnerability Scan checks your internet-facing systems for known issues so you can prioritise what to patch.
What an attacker can see: a Recon Scan shows the domains, services and systems of yours that are visible from outside, which helps you spot the forgotten ones.
Supplier risk: Supply Chain Risk helps you see the exposure of the third parties you rely on.
Stolen logins: a Dark Web Scan checks whether your business credentials have turned up in leaked data.